> For the complete documentation index, see [llms.txt](https://doc.dastra.eu/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://doc.dastra.eu/en/features/settings/roles-et-permissions.md).
# Roles and permissions
Every organization is different, so roles and permissions are extremely flexible in Dastra.
## General Functioning
Each user can be associated with 1 or more roles. The roles are themselves associated with a list of permissions (e.g.: write in the registry, post a request to exercise a right...). There are two ways to manage the roles associated with users.
* If you are an owner, you can use [this account management interface](https://app.dastra.eu/general-settings/users?q=\&page=1\&size=20)
* If you have the role of entity administrator, you can manage the roles and permissions of users belonging to your entity using [this interface](https://app.dastra.eu/general-settings/roles).
## Create your own roles
To create your own roles associated with permissions, go to [this page](https://app.dastra.eu/general-settings/roles).
You can create a custom "new role" by clicking on the "Create a new role" button\
It is possible to select the boxes associated with permissions
Creating a role
\
**Read/Write own elements:** Users can only view and edit items assigned to them within the module.
**Read:** Users can view all items in the module.
**Write:** Allows modification of all existing items in the module. In modules that offer the **Create** permission, Write does not grant the right to create new items.
**Create:** Allows users to create new items in the module. This permission is independent of the **Write** permission.
**Export:** Permits exporting all items.
**Import:** Allows importing all items into the module.
**Notification:** Users receive notifications for all items in the module.
{% hint style="info" %}
It is not possible to select both “Read/Write own elements” and permissions on all items for the same role in a module, except for the “Create” permission. Users access either only their own items or all items; the “Create” permission additionally lets them create new items.
{% endhint %}
\
Once you've created your custom role, you can assign it to any workspace user within your organization.
### Create permission
The following modules offer a **Create** permission that is separate from the **Write** permission:
* Task management
* Data processing records
* Data protection right request
* Data breach
* Data mapping and repositories
* Contracts management
* AI systems management
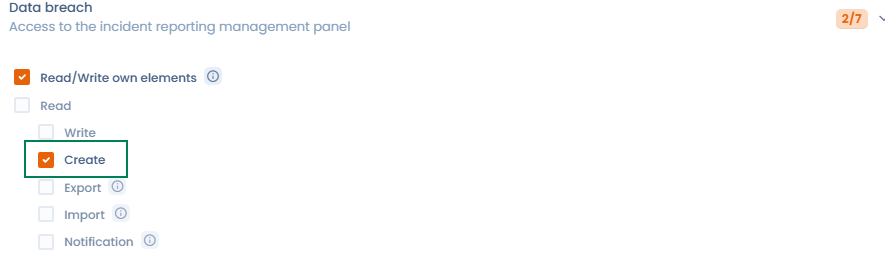
In these modules, **Create** can be checked together with **Read** or with **Read/Write own elements**. A role that combines **Read/Write own elements** and **Create** lets the user create new items and edit only the items assigned to them. For a role to edit existing items without creating new ones, check **Write** without checking **Create**.
The default **Administrator** and **Contributor** roles include the **Create** permission in these modules.
Create permission combined with editing own elements
## Clone an existing role
To save time when creating a new role based on an existing configuration, you can **clone a role** in a single click. Open the role you want to duplicate, then click **"Clone"**. A new role is created immediately with all the same permissions as the source role — simply rename it and adjust any permissions as needed.
This is particularly useful for creating variants of an existing role (e.g. a "DPO Contributor" role that is slightly different from a regular "Contributor") without starting from a blank canvas.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://doc.dastra.eu/en/features/settings/roles-et-permissions.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.