> For the complete documentation index, see [llms.txt](https://doc.dastra.eu/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://doc.dastra.eu/en/features/risk-management/risk-management-process.md).
# Risk management process
Learn how the risk management process works in Dastra.
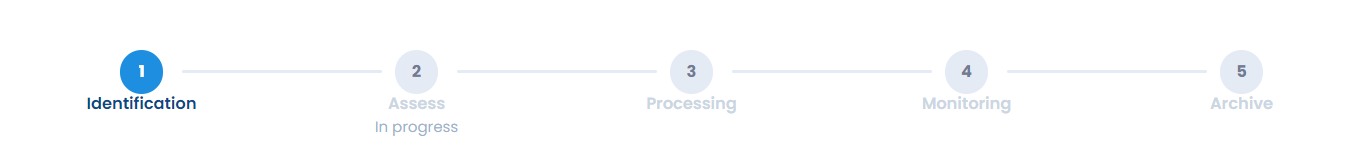
The Dastra risk management process is a simplified version of the eBios Risk Manager model and ISO 27005 risk assessment methodology. Manage your risks in 4 steps Risk management is a four-step process.
4 steps to risk management + archiving
1. **Identification** The aim of risk identification is to determine the events likely to occur, causing a feared event (such as a loss), and to provide an overview of how, where and when this event could occur.
2. **Assessment** Risk is assessed positively or negatively according to the level of impact the feared event presents, and the likelihood of it occurring, based on the threats that enable it.
3. **Processing** Risk management consists of responding to a risk. This can be of several kinds: risk reduction: measures must be implemented to reduce the risk risk acceptance: the organization accepts the risk as it is, without taking any measures to reduce it risk avoidance: the risk prevents the activity in question from being carried out risk transfer: the risk weighing on the organization can be transferred to another organization (via insurance, for example) risk-taking: the risk should be subject to mitigation measures, but the organization agrees not to implement them.
4. **Monitoring** Once the risk has been addressed, it is under control. This must be regularly reviewed and reassessed to take account of changes in the risk. In particular, when setting up control points.
Finally, **archive** your risks once they have disappeared, to keep a record of them.
The special feature of the Dastra risk management process is that it enables you to update your risk assessment in near-real time, based on the results of your control points.
{% hint style="info" %}
The unique feature of the Dastra risk management process is that it allows the risk assessment to be updated in near real time, based on the results of the checkpoints.
{% endhint %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://doc.dastra.eu/en/features/risk-management/risk-management-process.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.