> For the complete documentation index, see [llms.txt](https://doc.dastra.eu/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://doc.dastra.eu/en/features/compliance/library/threats.md).
# Threats
The threat library helps identify and document the causes or events likely to trigger a risk.
In Dastra, a threat represents the **triggering factor** of a risk:\
it describes *how* or *why* a risk can materialize.
Threats enrich risk analysis without making its assessment more complex.
***
## Threats, risks and controls: causal logic
The Dastra model is based on a simple and readable chain:
> **Threat** > **Risk** > **Controls** > **Tests**
* A **threat** describes a situation, a behavior or an event
* A **risk** describes the potential impact for the organization
* **Controls** aim to limit the occurrence or the effects of the risk
* **Tests** make it possible to verify the effectiveness of the controls
Example:
* **Threat**: lack of monitoring of AI logs
* **Risk**: information leakage through AI queries
* **Controls**: logging, monitoring, awareness training
* **Tests**: log review, periodic audits
***
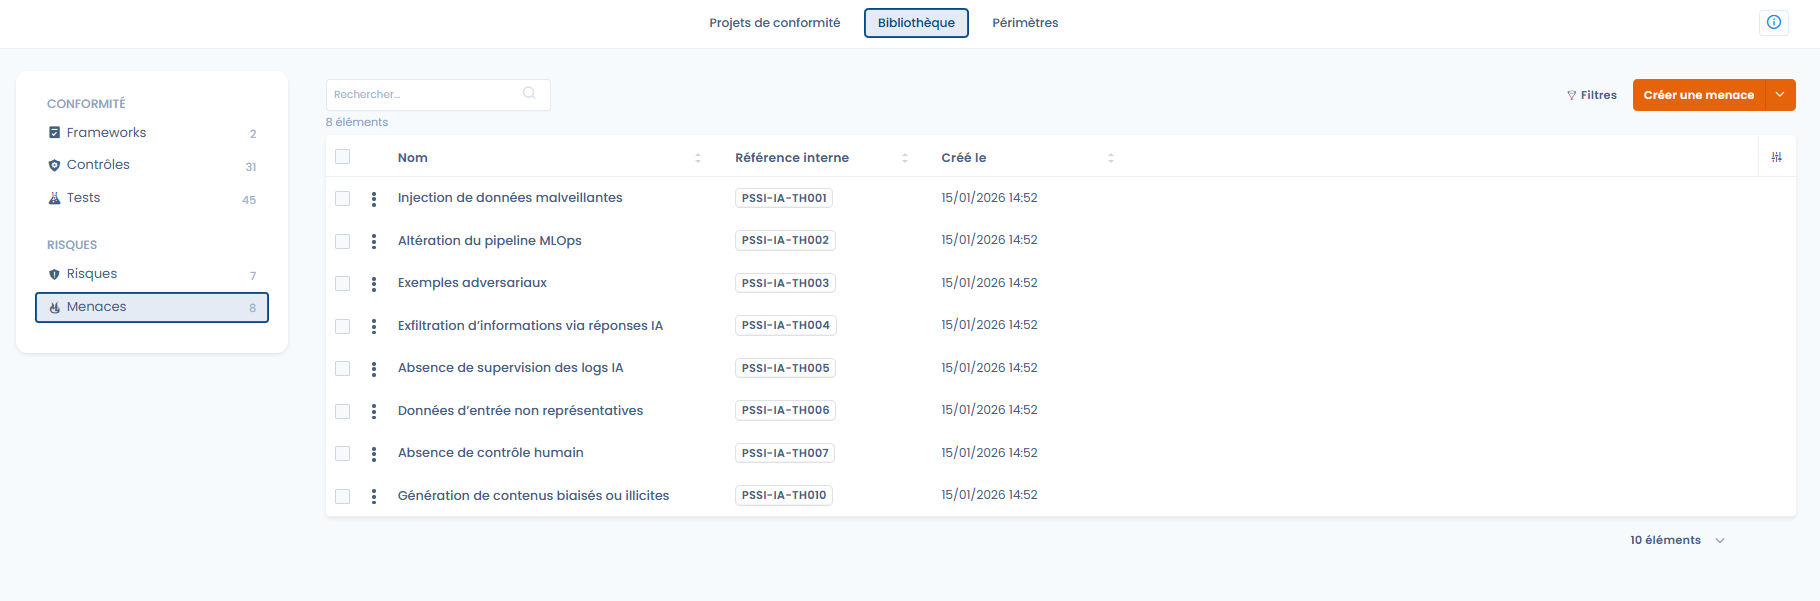
## Threat library view
The threat library centralizes all the identified threats, with:
* their name and reference,
* their creation date,
* filters to facilitate navigation.
This view makes it possible to:
* reuse existing threats,
* ensure consistent terminology,
* structure coherent risk scenarios.
***
## Creating and managing a threat
{% columns %}
{% column %}
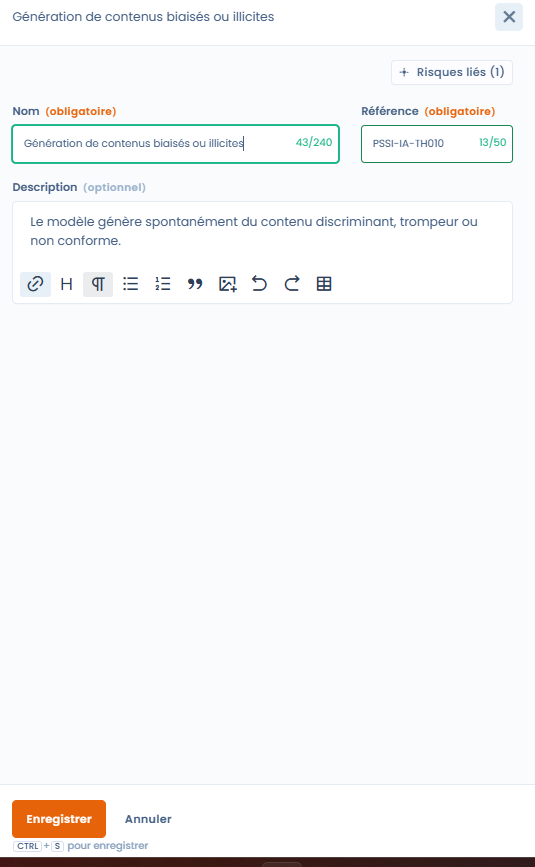
When creating or editing a threat, the user provides:
* **the name of the threat**
* **an internal reference**
* an **optional description** used to contextualize the threat
{% endcolumn %}
{% column %}
{% endcolumn %}
{% endcolumns %}
The module is deliberately **lightweight**:\
threats do not carry a quantified assessment and are not linked directly to controls.
***
## Association with risks
A threat is associated with **one or more risks**.
This association makes it possible to:
* precisely document risk scenarios,
* improve the understanding of causes,
* strengthen the consistency of the overall analysis.
The same threat can contribute to several risks, and vice versa.
***
## Why use threats
Using threats makes it possible to have:
* a finer and more realistic analysis of risks,
* better traceability of scenarios,
* clearer communication with stakeholders (CISO, DPO, business teams).
Threats complement the analysis without adding to the operational management burden.
***
## Merging threats
The threat library merges like the risk library: select at least two threats, then click **Merge** in the bulk actions, or in the edit window of a threat. Choose the **reference version** and the fields to carry over (see [Controls](https://doc.dastra.eu/en/features/compliance/library/controls.md)). The merge is irreversible.
***
## Summary
Threats are a **clarification tool**.\
They make it possible to better understand **the origin of risks**, and therefore to better justify the controls that are in place.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://doc.dastra.eu/en/features/compliance/library/threats.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.